Security
Cybersecurity, compliance, and the tools that carry it
EDR and XDR, zero trust, identity, and the SOC 2 and ISO 27001 work behind a contract.

Open-source security in the AI exploit era: patch without changing a thing
J.P. Morgan's Patchmageddon report puts median time from disclosure to exploitation at about one day in 2026, down from a year in 2021. For teams running open-source dependencies, patch cadence and inventory now decide exposure, not disclosure timing.

Abandoned software projects keep handing attackers a way in
A forgotten updater on 2.5 million Windows machines still trusted domains anyone could register. The cost of an inventory sweep is small next to the exposure of a dead project your stack still calls.

Four weak eMudhra keys broke any unpatched TLS connection
Cloudflare logged about 22,000 attempted handshakes with eMudhra's weak intermediate keys in a week and patched its own edge within hours. For an estate that ships its own CA bundle, the fix is a software update, not a revocation feed.
Firewalls at the edge: what Cloudflare, Cloud Armor and Fastly charge per million requests
Every WAF bills a base fee, a per-request charge and a per-rule charge, and the request count decides which one is cheapest. Fastly's packages publish a monthly price and a request ceiling; Cloudflare and Cloud Armor publish neither here.
DLP on the endpoint: what Purview and Netskope charge for a thousand users
Purview's DLP is sold through Microsoft 365 E5, the Purview Suite or pay-as-you-go, and the endpoint controls arrive with the licence. Price 1,000 users across the bundles and check what the standalone endpoint DLP adds.
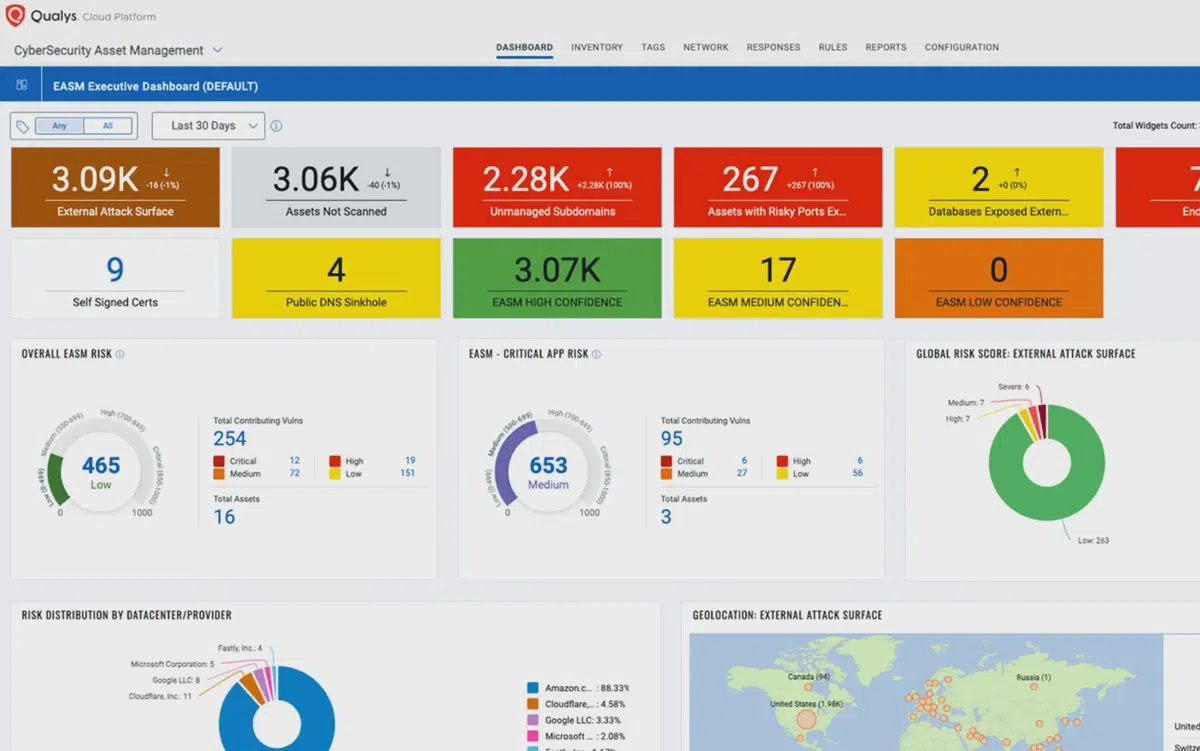
How much vulnerability management costs for 5,000 assets: Qualys, Tenable and Rapid7 priced
All three price by asset or scan target, and the modules are where the bill grows: cost the base platform plus the two modules a 5,000-asset estate actually needs, and give the asset count where each vendor's per-asset price stops being the cheapest.
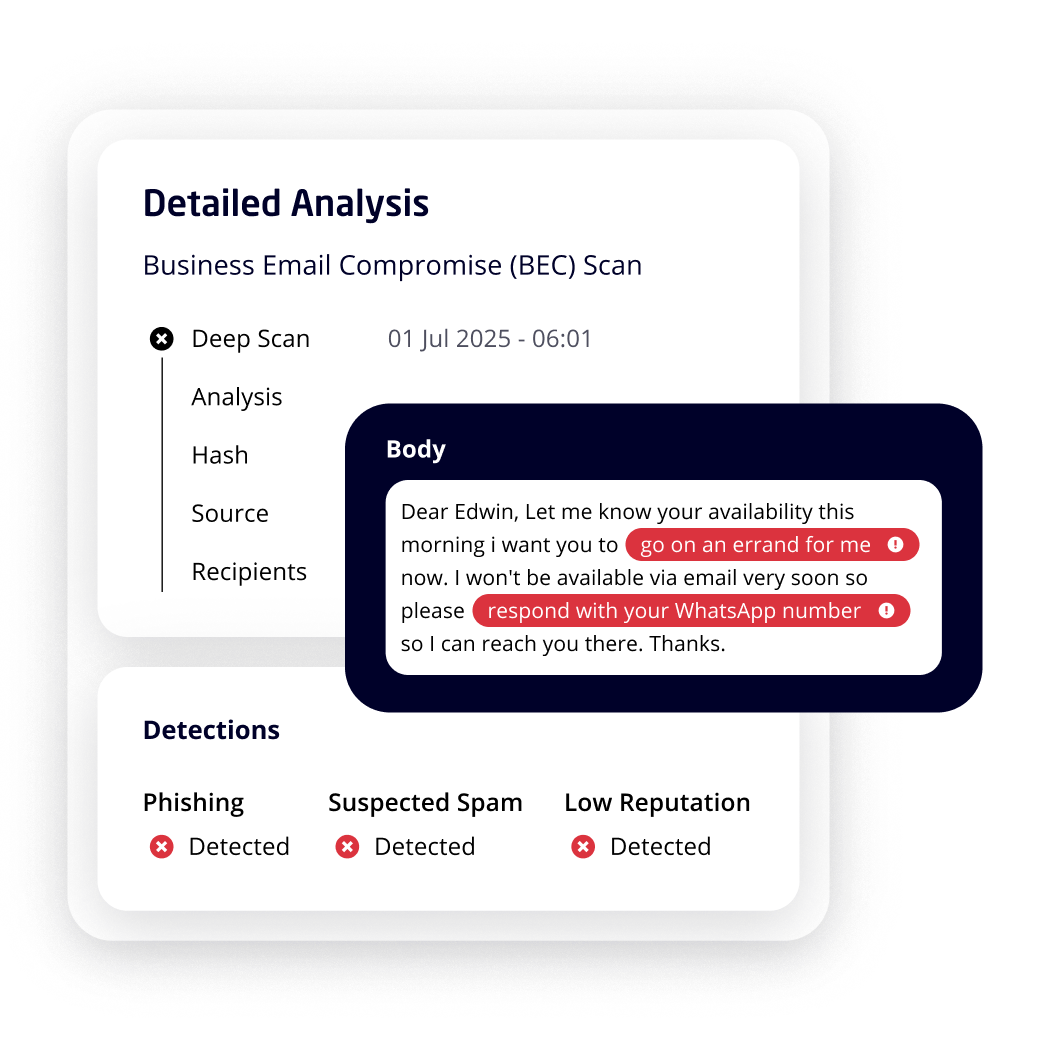
Mimecast vs Abnormal vs Barracuda: what email security costs per mailbox at 2,000 seats
All three publish list prices that only make sense once the add-ons are counted: price 2,000 mailboxes with link protection and the archive each product charges separately, and give the mailbox count where the platform already inside Microsoft 365 stops being…
Replacing a VPN with ZTNA: what the per-user licence buys at 1,000 staff
ZTNA is priced per user with a connector and a policy tier: cost 1,000 users across the two common models, count what the existing VPN already covers for free, and give the user and app counts where the zero-trust suite is the cheaper bundle.
Ten thousand secrets: what Secrets Manager, Key Vault and Secret Manager charge
AWS Secrets Manager bills $0.40 per secret per month plus $0.05 per 10,000 API calls, and a 10,000-secret estate making 12 million calls a month lands near $4,000 plus $60. Azure Key Vault and Google Secret Manager publish their own meters, so the rotation…
Zscaler vs Netskope vs Prisma Access: what SSE costs at 1,000 users
Zscaler, Netskope and Prisma Access all quote per user and none publishes a rate. Vendr's 2026 deals put the full SASE band at $35 to $80 a user a month, and the bundle decides how much ZTNA, CASB and DLP is included.
CrowdStrike Falcon Complete vs SentinelOne Vigilance vs Arctic Wolf
SentinelOne publishes a per-endpoint list price and a $1M warranty; CrowdStrike publishes a one-minute median containment; Arctic Wolf publishes neither and sells a $3M warranty. None of the three publishes a response-time SLA on its service page.
Sentinel vs Splunk Cloud vs Google SecOps: what 50 GB a day costs for three years
Three platforms meter three different things and two of them publish no rate. For a 1,000-employee estate the three-year number turns on where the logs are born, not on the headline price.
OWASP moved agency to third place: the checklist an AI agent must pass before approval
Excessive agency climbed three places and unbounded consumption four in OWASP's 2026 LLM list. An approval now has to test identity, tool scope and spend as three separate controls.
The post-quantum gap is signatures, and the 2030 deadline belongs to your inventory
MITRE rated eight enterprise technologies: key establishment ships in five, signatures in two, and none reaches FIPS 140-3 validation. US federal deadlines now sit in 2030 and 2031.
The CRA clock starts at 24 hours: what to ask a software vendor now
Since 11 September 2026 a manufacturer selling into the EU must report an exploited vulnerability through ENISA's platform within 24 hours. The contract clause is the buyer's only lever.
EDR vs MDR at 2,000 endpoints: buying the tool or buying the team
EDR is a per-endpoint licence; MDR is that licence plus an analyst contract. CrowdStrike publishes no price for either, so the decision turns on the internal hours a 24/7 rota needs and what the vendor quotes for the managed tier.
NIS2 and DORA: what compliance actually costs a 500-employee supplier
Both regimes price compliance in controls and evidence, not licences: NIS2 adds incident reporting and board accountability, DORA adds ICT third-party oversight. A 500-employee supplier usually needs one regime, not two.
Okta vs Entra ID: what SSO covers and what SCIM provisioning still costs
SSO is the cheap half of identity; provisioning is where the per-user price climbs. Okta's Starter Suite starts at $6 and Essentials at $17 per user/month, while Entra ID P1 and P2 are sold per licence or bundled into Microsoft 365 E3 and E5.
API security: what an API gateway already covers and what the specialist tier adds
Amazon API Gateway bills per million calls with no minimum fee, so a 200-API estate pays for traffic, not API count. The protections it does not document are what a per-API security product sells.
CyberArk vs BeyondTrust vs Delinea: what privileged access costs per admin seat
CyberArk's published pricing page carries no per-seat figure, and the platform is now being rebranded Idira under Palo Alto Networks. Price the three on seat count and ask each vendor for the tier boundary in writing.
Oracle's October CPU: 1,295 patches and six 10.0 flaws that need no password
Oracle's October Critical Patch Update ships 1,295 patches, six of them scored 10.0 and all reachable without credentials. A finance estate on EBS, SOA Suite and Access Manager can retire five of the six in two maintenance windows.
CrowdStrike vs SentinelOne for the 1,000 to 5,000 seat estate
CrowdStrike correlates detections in a cloud threat graph; SentinelOne runs behavioral AI and rollback on the agent. Offline working and Microsoft's E5 bundling usually settle the choice.
Zero trust in twelve months: the sequence that works for 2,000 people
Zero trust is an architecture, not a purchase. Identity, device trust, segmentation, workload identity and data controls each depend on the last, and the phase that stalls is usually the one nobody staffed.
Vanta vs Drata vs Secureframe: what the tool automates, and what your auditor still owns
The three big compliance automation platforms collect evidence and monitor controls, but none of them issues a SOC 2 report. Here is what each charges for, where the auditor fee sits, and which one fits your estate.
SOC 2 Type II evidence: the controls auditors test and what proof costs
Most Type II findings are missing evidence, not missing controls. The control-to-evidence map for access, change, monitoring and subprocessors, the published cost of continuous collection, and the window length that fits the deal.
Phishing-resistant MFA: plan the rollout by cohort, not by department
Push prompts and SMS codes fall to a live phishing proxy; FIDO2 keys and passkeys do not. A cohort-by-cohort rollout plan, the temporary pass that bootstraps it, and the metric that proves the change held.
Advertisement